CERTIFICATE_VERIFY_FAILED на российском API: как доверять сертификату Минцифры только в одном клиенте Python
A Russian API server is signed by a chain from the Ministry of Digital Development, and Python fails with CERTIFICATE_VERIFY_FAILED. The article shows how to trust that certificate in a single client using a custom SSLContext, an intermediate certificate as the anchor, and the VERIFY_X509_PARTIAL_CHAIN flag, without verify=False or adding the root to the system. It covers the risks of this flag, how to do the same in aiohttp, httpx, requests, and urllib, and how to verify the fingerprint. It also explains what to do when the certificate changes.
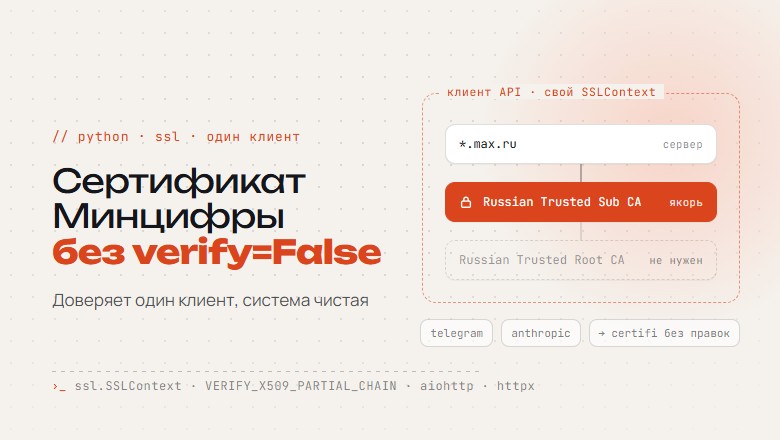
Сервер российского API подписан цепочкой Минцифры, и Python падает с CERTIFICATE_VERIFY_FAILED. Показываю, как доверять этому сертификату ровно в одном клиенте: свой SSLContext, промежуточный сертификат как якорь и флаг VERIFY_X509_PARTIAL_CHAIN, без verify=False и без корня в системе. Чем рискуешь с этим флагом, как то же сделать в aiohttp, httpx, requests и urllib, как сверить отпечаток и что делать при смене сертификата. Читать далее